Managed DNS and anycast network

DNS that answers first

ShieldNS runs authoritative DNS on a global anycast network with DDoS scrubbing at every location, so your domains resolve fast and stay up when someone tries to take them down.

  • 100% uptime SLA
  • 65 anycast PoPs
  • Anycast DDoS shield
$ dig example.com A +nsid @ns1.shieldns.compreview
TypeTTLAnswer
A300203.0.113.10
AAAA3002001:db8::10
NS3600ns1.shieldns.com.
NS3600ns2.shieldns.com.
6 msFRA
9 msIAD
12 msRUH
14 msSIN
Answered from 65 PoPsSample answers from documentation ranges

Products

Five products on one network

Start with managed DNS and add protection, geographic routing or a dedicated network when you need them. Every plan is paid, so every customer gets the same network and support.

Compare plans

Managed DNS

Premium anycast DNS for every zone you run. DNSSEC, secondary DNS, reverse zones, ALIAS records, dynamic DNS, mail forwarding and web redirects, all managed from one panel or the API.

Example zone records
TypeNameTTLValue
Aexample.com.300203.0.113.10
AAAAexample.com.3002001:db8::10
CNAMEwww3600example.com.
MXexample.com.360010 mail.example.com.
TXTexample.com.3600"v=spf1 include:_spf.example.com -all"
SRV_sip._tcp360010 60 5060 sip.example.com.
CAAexample.com.864000 issue "letsencrypt.org"
Explore managed DNSfrom $8.95/mo

Anycast network

Every query, answered nearby

One IP address, announced from 65 PoPs in 52 cities on six continents. Each query lands at the closest point of presence, and if a location goes dark, traffic moves to the next one within seconds.

See all locations
65PoPs
In 52 cities worldwide
18ms
Median query response
6continents
Covered by the same network
100%
Uptime SLA on every plan

Select a region to list its locations.

Resolution and DDoS scrubbing

What happens to every query

Legitimate queries and attack traffic arrive at the same edge. Only one of them reaches the authoritative engine.

How ShieldNS resolves queries and scrubs attack trafficLegitimate queries from resolvers reach the nearest anycast location, pass the scrubbing layers and are answered by the authoritative engine. Attack traffic is split across locations and dropped at the scrubbing layer. Signed answer returns to the resolver ResolversISP and public resolversasking for your records Attack sourcesFloods, reflection,botnets, spoofed IPs 01 ANYCAST EDGENearest locationBGP anycast sends eachpacket to the closest of65 PoPs, so attackvolume is split up. 02 ScrubbingFiltered at every PoP L3 / L4SYN, UDP, reflection floods Rate and reputationPer-source query limits L7 DNSMalformed, random-subdomain Attack traffic dropped here 03 AnswerAuthoritative engineLooks up your zone andreturns a DNSSEC-signedanswer. 18 ms median How ShieldNS resolves queries and scrubs attack traffic ResolversISP and publicresolvers AttacksFloods, reflection,botnets 01 ANYCAST EDGENearest locationBGP anycast sends each packet tothe closest of 65 PoPs, so attackvolume is split up. 02 ScrubbingFiltered at every PoP L3 / L4SYN, UDP, reflection floods Rate and reputationPer-source query limits L7 DNSMalformed, random-subdomain Attack traffic dropped here 03 AnswerAuthoritative engineLooks up your zone and returns aDNSSEC-signed answer. 18 ms median
  • Legitimate query
  • Signed answer
  • Attack traffic
A long data centre aisle between server racks, lit in blue
Edge location, operational

Infrastructure for the queries that matter

  • Redundant by designEvery location runs multiple name servers on diverse transit, and every zone is served from all of them.
  • Signed and verifiedDNSSEC signing and key rollovers happen automatically; you add one DS record at your registrar.
  • Watched around the clockOur network operations centre monitors every PoP from inside and outside the network, 24 hours a day.

Pricing

Plans for every zone count

Starter

$8.95/mo

Billed monthly

For a handful of production domains.

  • 5 DNS zones
  • 200 records
  • 5M queries / month
  • DNSSEC one-click signing
Choose plan

Business

$44.95/mo

Billed monthly

For portfolios and high-traffic platforms.

  • 400 DNS zones
  • 20,000 records
  • 500M queries / month
  • 3 monitoring checks
Choose plan

Enterprise

Custom

Annual contract

Dedicated anycast, vanity name servers and a named engineer.

  • Unlimited zones and records
  • Dedicated anycast network
  • Vanity name servers
  • 100% uptime SLA
Talk to sales

Prices in USD, excluding tax. DDoS Protected DNS starts at $17.95/mo and GeoDNS at $29.95/mo. See every plan and limit.

For developers and sysadmins

Automate every record

Everything in the panel is in the API. Manage zones from your CI pipeline, keep DNS in Terraform next to the rest of your infrastructure, and update home or office IPs with one request.

  • REST API with scoped tokens, for zones, records, DNSSEC and health checks.
  • Terraform provider to review DNS changes in pull requests.
  • BIND import and AXFR to move existing zones without retyping them.
  • Dynamic DNS that works with routers, scripts and cron.
# Add an A record to example.com
$ curl -X POST https://api.shieldns.com/v1/zones/example.com/records \
    -H "Authorization: Bearer $SHIELDNS_TOKEN" \
    -H "Content-Type: application/json" \
    -d '{"type":"A","name":"www","content":"203.0.113.10","ttl":300}'

{
  "id": "rec_8f2c41",
  "type": "A",
  "name": "www.example.com.",
  "content": "203.0.113.10",
  "ttl": 300,
  "status": "live on 65 PoPs"
}
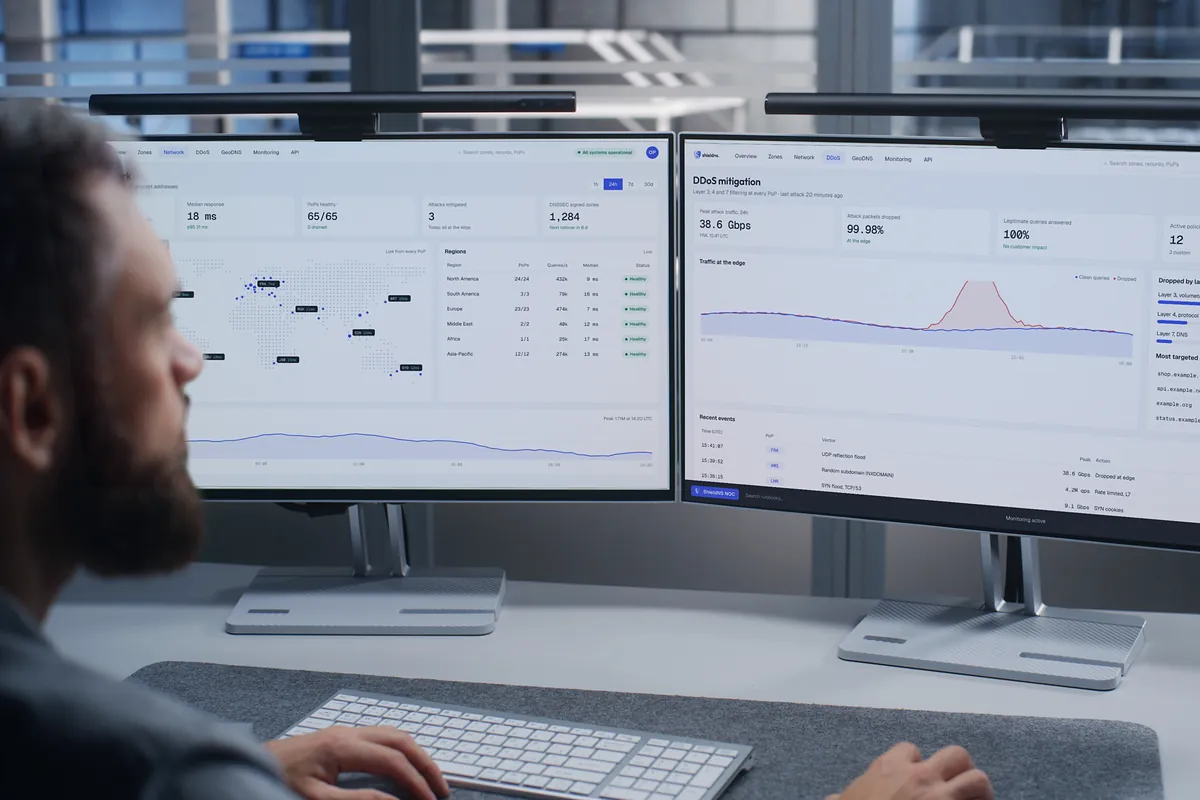
An engineer watching the ShieldNS anycast network and DDoS dashboards on two monitors
NOC, 24/7

Enterprise anycast

A network that carries your name

For banks, registrars, SaaS platforms and anyone whose DNS is part of the product. Your own anycast addresses, your own name server hostnames, and engineers who already know your setup.

  • Dedicated anycastIP space and announcements used only by your zones.
  • Vanity name serversns1.example.com on your own domain.
  • 100% uptime SLAService credits written into the contract.
  • 24/7 NOC engineers15-minute response, a named contact and a dedicated phone line.

FAQ

Questions engineers ask us

Can't find your answer? Our engineers reply around the clock.

How long does DNS propagation take?

Changes you make on ShieldNS reach every anycast location within seconds. What visitors see after that depends on caching: resolvers keep the old answer until its TTL expires. Lower the TTL on records you plan to change (for example to 300) a day ahead, make the change, then raise it again.

Name server changes at your registrar are slower, because the parent zone (for example .com) publishes NS records with a 48-hour TTL. Most resolvers pick up the new delegation within a few hours.

How do I move my zones from another DNS provider?

Three ways, depending on what your current provider allows:

  • Zone transfer (AXFR). Allow transfers to our import servers and we pull the zone, including every record type.
  • BIND file import. Upload a zone file in the panel or send it to POST /v1/zones/{zone}/import.
  • Secondary first. Run ShieldNS as a secondary alongside your current primary, check the answers match, then switch the NS records at your registrar.

Nothing changes for visitors until you update the name servers at your registrar.

How do I turn on DNSSEC?

Enable DNSSEC on the zone and we generate the keys, sign every record and re-sign automatically, including key rollovers. We then show you a DS record (algorithm 13, ECDSA P-256). Add it at your registrar, and validating resolvers start checking your answers within the parent zone's TTL.

If you register the domain with us, we publish the DS record for you.

How much attack traffic can ShieldNS absorb?

Capacity is spread across every anycast location, so an attack is split between the locations nearest its sources instead of landing on one data centre. Each location filters volumetric floods at layers 3 and 4, applies per-source rate limits, and drops malformed and random-subdomain DNS floods at layer 7 before they reach the authoritative engine.

For current per-region capacity figures and custom mitigation policies, talk to our network team.

What does the 100% uptime SLA cover?

Every paid plan is backed by a 100% uptime SLA for DNS resolution: if our anycast network fails to answer queries for your zones, you receive service credits, as set out in our service level agreement. Planned maintenance never takes resolution offline, because we drain one location at a time.

Move your DNS to an answer you can trust

Import a zone in minutes, check every answer before you switch, and only then change your name servers.